Cloud Security & Compliance
Secure and optimize your cloud with Aplus Technology’s Cloud Security & Compliance Services. We provide data protection, compliance, threat detection, and risk managementto safeguard your business.
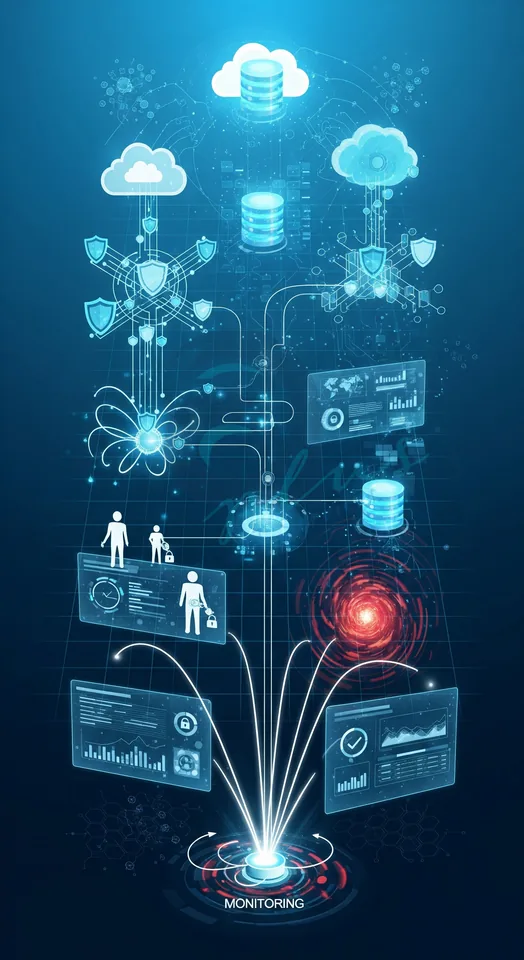
What We Do:We help organizations secure their cloud environments and maintain compliance with industry standards. Our services protect sensitive data, ensure privacy, and reduce the risk of cyber threats.
How We Do It:Our team implements advanced security protocols, identity and access management, and continuous monitoring to safeguard cloud assets and prevent unauthorized access.
Data Protection:We provide encryption, backup, and secure storage solutions to maintain the integrity and confidentiality of your cloud data.
Compliance & Auditing:Our experts ensure that your cloud infrastructure complies with GDPR, ISO, HIPAA, and other relevant regulations through regular audits and best practices.
Threat Detection:Proactive monitoring and advanced threat detection systems identify vulnerabilities and potential breaches before they impact your operations.
Risk Management & Governance:We offer detailed risk assessments, policy implementation, and continuous improvement strategies to maintain a secure, compliant, and resilient cloud ecosystem.
Zero-Trust Identity & Access Management (IAM): Enforce least-privilege RBAC, SSO/SAML/OIDC federation, hardware MFA, and just-in-time privileged access across AWS, Azure, GCP, and internal enterprise apps.
Cloud Security Posture Management (CSPM) & SIEM: Continuous automated scanning to detect misconfigured S3/storage buckets, exposed ports, unencrypted volumes, and IAM drift with real-time SIEM threat correlation.
End-to-End Encryption & Secrets Management: Protect data at rest (AES-256 / customer-managed KMS keys) and in transit (TLS 1.3 / mTLS), backed by centralized HashiCorp Vault or cloud KMS key rotation.
Regulatory Audit Readiness (GDPR, ISO 27001, SOC 2 & HIPAA): Automated compliance evidence collection, data residency enforcement for EU and Indian jurisdictions, penetration testing, and remediation roadmaps.
Architect regional data partitioning, automated PII anonymization, and cryptographic erasure workflows for cross-border enterprise platforms.
Immutable air-gapped cloud backups, automated WORM storage policies, and quarterly recovery drills guaranteeing rapid RTO and RPO objectives.
Shield public-facing portals and ERP APIs against OWASP Top 10 exploits, credential stuffing, botnet scraping, and volumetric DDoS attacks.