Cloud, DevOps & Automation
Accelerate innovation with Aplus Technology’s Cloud, DevOps & Automation Services. We provide cloud migration, CI/CD, infrastructure automation, and optimized IT operationsto help businesses scale faster and reduce costs.
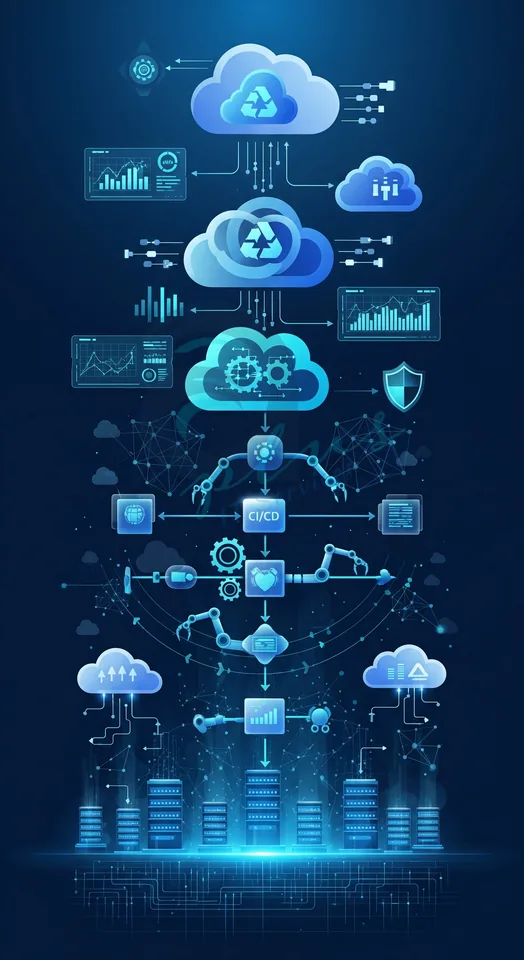
What We Do:We enable organizations to adopt cloud infrastructure, implement DevOps practices, and automate workflows to increase agility and operational efficiency.
Cloud Services:From cloud migration and deployment to hybrid and multi-cloud strategies, we ensure secure, scalable, and optimized cloud environments.
DevOps Implementation:We establish continuous integration, continuous delivery (CI/CD), and robust monitoring pipelines for faster, reliable software releases.
Automation:Automating infrastructure provisioning, configuration management, and business workflows reduces manual errors and accelerates delivery timelines.
Integration:Seamless integration of cloud platforms, DevOps tools, and automation frameworks ensures consistent deployment and operational visibility.
Security & Compliance:Our services include cloud security best practices, access control, and compliance frameworks to safeguard business-critical data and systems.
GitOps & Automated CI/CD Release Pipelines: Zero-touch build, test, security scan (DevSecOps), and blue/green or canary deployments engineered with GitHub Actions, GitLab CI, Jenkins, and ArgoCD.
Kubernetes (EKS, AKS, GKE & On-Premise) Orchestration: Production-grade container clusters with Helm charts, horizontal pod autoscaling, Istio/Linkerd service mesh, and automated SSL/ingress management.
Infrastructure as Code (Terraform, Pulumi & Ansible): Version-controlled, reproducible cloud environments eliminating configuration drift across development, staging, and multi-region production clusters.
Full-Stack Observability & Automated Incident Response: Unified metrics, logs, and distributed tracing using Prometheus, Grafana, OpenTelemetry, ELK Stack, and Datadog with PagerDuty/Slack alert routing.
Transform manual weekend deployment cycles into 20+ automated, zero-downtime production releases per day with instant 1-click rollback safety.
Active-active container orchestration across EU and APAC cloud regions delivering 99.99% uptime and automatic failover during cloud zone outages.
Embed container vulnerability scanning (Trivy/Snyk), SAST/DAST checks, and HashiCorp Vault secrets management directly into every pull request.